What device encryption actually protects
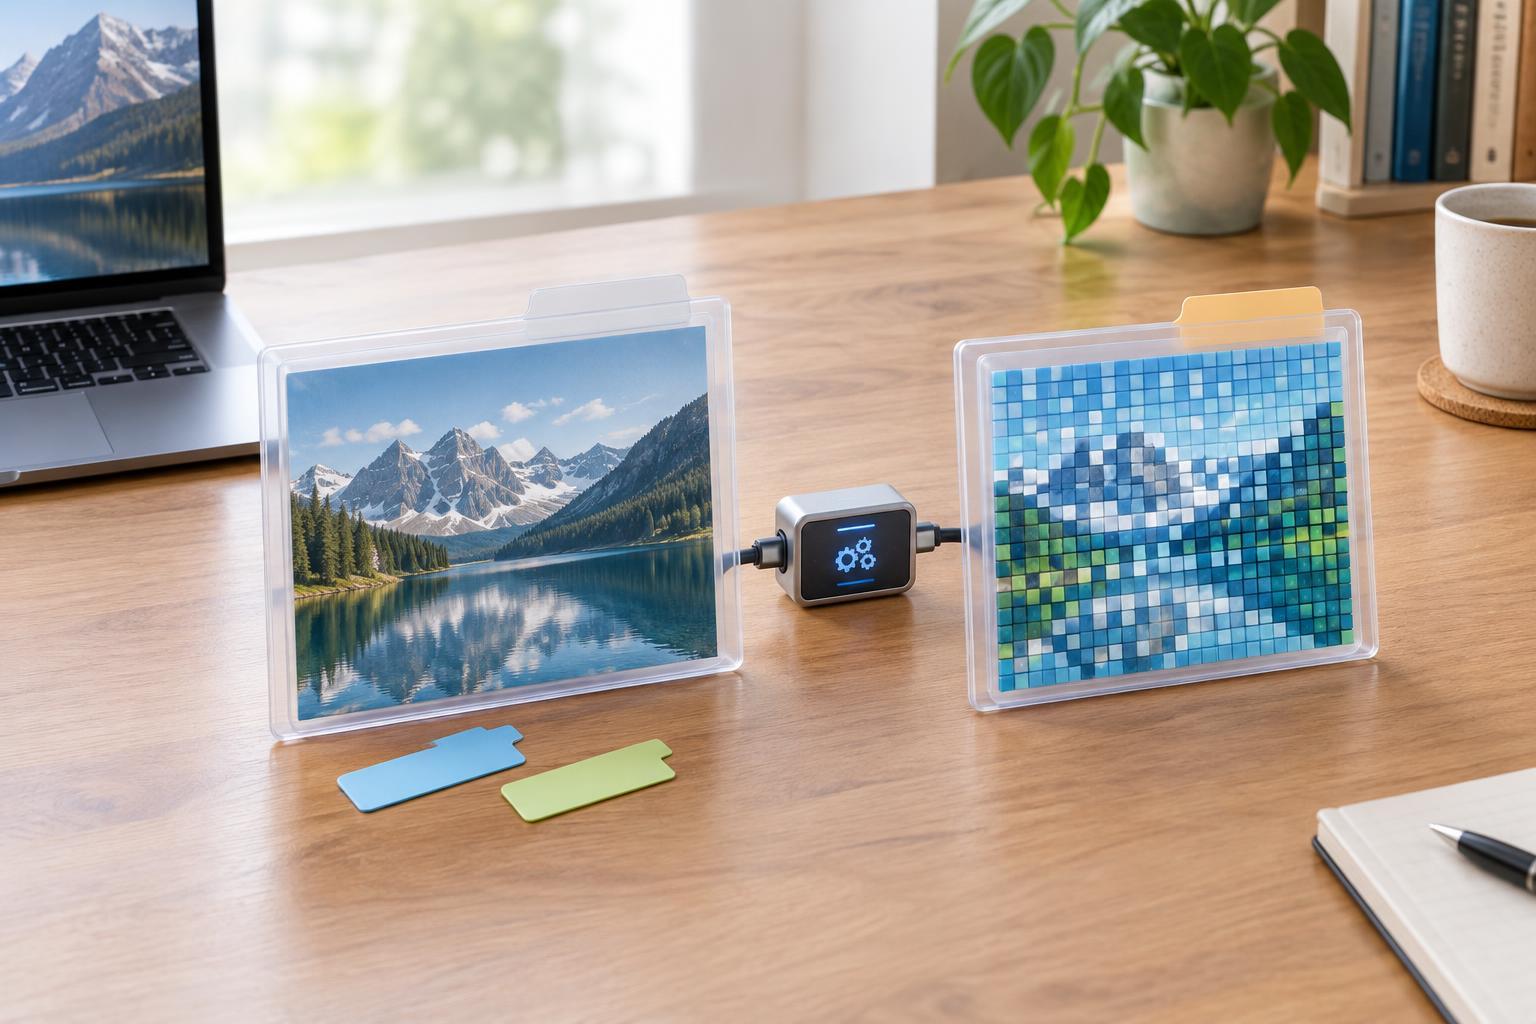
Device encryption turns stored information into data that cannot be read without the right cryptographic key. On a laptop or phone, this usually means encrypting the device’s internal storage. If someone removes the storage drive or tries to read it using another computer, they should not be able to browse your documents, photos, saved messages, or other files simply by connecting it.
Encryption is especially useful when a device is lost or stolen because physical possession alone does not grant access to its contents. It protects data at rest: information stored on the device while access to it is locked. It does not make a stolen laptop or phone impossible to use, and it does not erase copies of your information stored elsewhere, such as in a cloud account or on an unencrypted backup drive.
Why the lock screen and device state matter
The protection you get depends partly on whether the device was off, locked, or already in use when it disappeared. A powered-off, encrypted device with a strong sign-in secret generally presents a harder obstacle than one that was left unlocked. On an unlocked device, someone may be able to open apps, read notifications, access signed-in accounts, or copy files without having to break the encryption.
A screen lock and encryption do different jobs. Encryption protects stored data from being read outside the normal sign-in process; the screen lock controls access through that process. Use a strong passcode or password, set the device to lock automatically after a short period of inactivity, and require authentication when it wakes. Biometric unlocking can be convenient, but a passcode or password remains an important fallback.
Check coverage before a device goes missing
Many recent phones encrypt internal storage by default, but it is still worth checking that a screen lock is enabled and that the device is receiving security updates. Laptops vary more by operating system, edition, hardware, and setup. Look in the device’s security or storage settings for full-disk or device encryption, and confirm that it reports protection as active. If you manage several computers, document which ones are encrypted rather than assuming they all share the same configuration.
Pay attention to storage that encryption may not cover. Removable memory cards, USB drives, external disks, and exported backups can have separate settings. A laptop’s encrypted internal drive will not protect a spreadsheet copied to an unencrypted USB stick. If you keep sensitive files on removable media, encrypt that media too, or avoid storing those files on it.
If encryption provides a recovery key, save it somewhere secure and separate from the device. A recovery key may be needed after certain account, hardware, or system changes. Losing it can mean losing access to your own files. Do not keep the only copy in a note on the encrypted device.
Encryption has limits beyond local storage
Encryption cannot compensate for an easy-to-guess password or a device left open in a public place. It also does not stop someone from using an account that was already signed in on another device. A person who learns your account password through phishing may be able to reach synchronized files without touching the lost hardware. Keep account passwords unique and enable multifactor authentication where available.
Remote location, locking, and wiping features can add options after a loss, but they depend on the device being configured in advance and often need it to connect to a network. A wipe request is not a substitute for encryption: you may not know whether the device received it. Backups serve a different purpose. They help you recover your work, while encryption helps keep a stranger from reading the missing copy.
What to do if a laptop or phone is lost
Start by checking whether the device is genuinely missing, then use any built-in device-finding service to mark it as lost or lock it if that option is available. Change passwords for important accounts if the device was unlocked, its sign-in details may have been exposed, or you notice suspicious activity. Review account sessions and sign out of the missing device where the service allows it. For a work device, notify whoever manages its security promptly so they can apply the organization’s procedures.
If recovery seems unlikely, consider a remote wipe, understanding that it may not run until the device comes online and may end your ability to locate it. The best protection is already in place before the loss: active encryption, a strong lock, protected accounts, secure recovery-key storage, and a usable backup. Together, those measures make a missing device an inconvenience rather than automatically an exposure of everything stored on it.